Deliverd ❤️ Microsoft: better together
25 October 2026 · Deliverd Engineering Team · 5 min read
Most of the enterprises we talk to have already picked their AI platform, and very often it is Microsoft. Copilot is in Word and Teams. Makers build agents in Copilot Studio. Developers ship with GitHub Copilot, Foundry and Agent Framework. Agent 365 keeps the inventory. That is a lot of agents, built by a lot of people, and most of them will touch real data and real customers.
We don't think the answer is a second platform. Microsoft runs your agents. Deliverd decides what they may do, and proves who said yes. The two fit together, and this post is about where.
What each side brings
Microsoft gives you the place agents are built, run, secured and listed. Identity through Entra, security signals through Defender and Sentinel, data protection through Purview.
Deliverd gives you the decisions in between. Before an agent does something that matters, it asks: your organisation's rules answer first, and a named person answers the rest, in Teams, Outlook, Slack or on their phone. Before an agent sends data somewhere, Deliverd Screen checks what is in it against what your AI register approves. And every answer is kept in a tamper-evident record your auditors can check for themselves.
Nobody on the Microsoft side holds "why was this AI use allowed, who signed off this action, on what evidence". That is the gap we fill.
New: Screen on by default for every Copilot Studio agent
The question we hear most from IT and risk teams is simple. "Our people are building agents every week. How do we make sure every one of them is screened, without asking every maker to remember?"
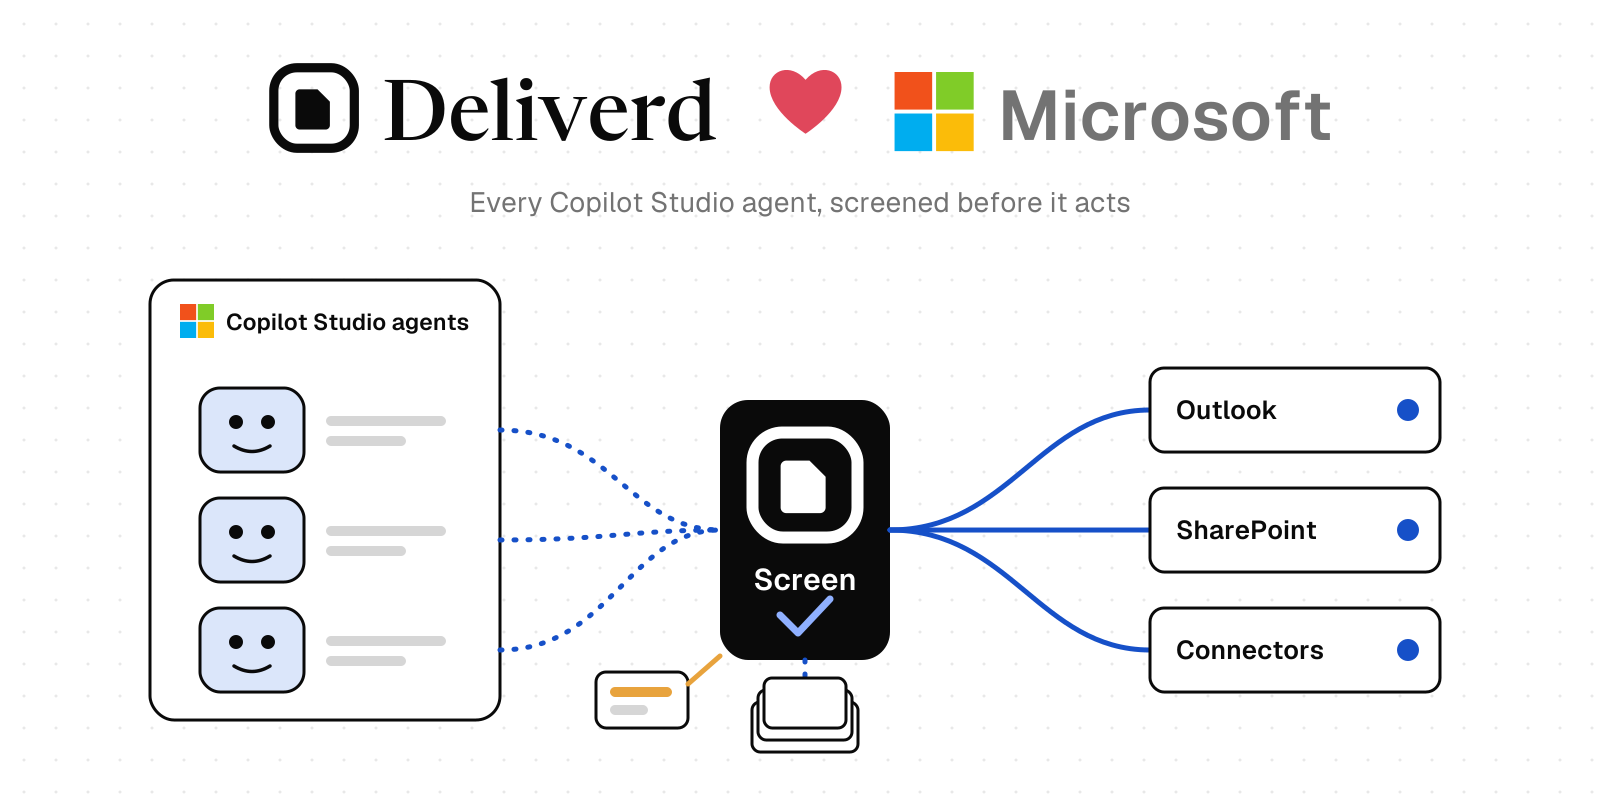
Copilot Studio has an answer built in: external threat detection, currently in preview. An administrator points an environment at a provider, and from then on Copilot Studio asks that provider before every tool call of every generative agent in that environment. Deliverd is now one of those providers.
Here is what that means in practice:
- Every agent, from its first tool call. Including the agent someone builds next Tuesday. Nobody adds a tool, edits an agent or reads a guide.
- Your policy, not a generic one. Deliverd screens what the agent is about to hand the tool (an email body, a file, a record) for personal data, secrets and your own confidential terms, against the data your AI register approves for those tools.
- You choose how hard it bites. Watch records every finding and blocks nothing, which is where we suggest starting. Block what the policy refuses stops the clear cases, such as an API key in an email. Strict also stops anything your policy would redact or put to a person, because a tool call can't be redacted halfway or held while someone decides. Secrets are refused by default.
- One stop button. If something goes wrong, pressing stop in Deliverd blocks every Copilot Studio agent's tool calls until a person resumes them.
- A record, not just a block. Every call with a finding, and every block, lands in Deliverd's data screening checks and audit trail with the agent, the tool and the verdict. Never the data itself.
Setting it up takes about twenty minutes: an app registration in Entra (Microsoft provides the script), the tenant and app ID in Deliverd, and the endpoint pasted into the Power Platform admin center for each environment. Start with your default environment, where most agents are made.
Where it stops
We would rather you hear the limits from us.
- Microsoft sets this up per environment. There is no single switch for a whole tenant, so each new environment needs pointing at Deliverd once.
- It covers generative agents. Copilot Studio skips classic agents.
- Copilot Studio waits about a second for an answer. If none comes, it applies the error behaviour you chose: let the call run, or block it. For calls that must never go unscreened, choose block.
- Agents made inside Microsoft 365 Copilot itself are protected by Microsoft Purview, not by this hook.
- Screen finds email addresses, card numbers, IBANs, national identifiers and secrets well. It does not reliably find names. Treat it as fewer identifiers sent and a record of what was, not as proof that nothing sensitive left.
The rest of the Microsoft picture
Screening is one piece. Across the Microsoft stack, Deliverd also brings:
- Approvals in Teams. A person approves or declines from a card in Teams, and the decision is recorded under their name.
- Microsoft 365 Copilot and Copilot Studio over MCP. Agents can request approvals, check gates and screen data with one remote MCP server.
- Power Automate and agent flows. A Power Platform connector, for the flows that can't call MCP.
- Foundry and Agent Framework. Adapters that put a person in front of an agent's tool approval, for Python and .NET.
- GitHub Copilot. Hooks that check a Deliverd gate before the coding agent runs a release or a destructive command.
- Entra Agent ID. Agents sign in with their own Entra identity instead of a pasted key.
- Agent 365 and Sentinel. The Agent 365 inventory feeds your AI register, and Deliverd decisions can flow to Sentinel.
Our Microsoft integrations are in preview while we finish testing them in customer tenants. If you run Copilot Studio and want screening switched on for your organisation, tell us and we'll set it up with you.
Deliverd is an independent product. It is not made or endorsed by Microsoft. We just think the two are better together.