Your SOC can now see what your agents were allowed to do
6 November 2026 · Deliverd Engineering Team · 4 min read
Ask a security team what they watch and the answer is usually "everything". Sign-ins, endpoints, email, cloud resources, all landing in one place, with rules that raise an incident when something looks wrong. For a lot of the organisations we talk to, that place is Microsoft Sentinel.
Then ask what they see of the company's AI agents. Usually the honest answer is: the API calls, maybe. Not what the agent asked to do. Not who said yes. Not the times the answer was no and the agent tried anyway.
That is exactly what Deliverd records. So this week we've built the bridge: Deliverd for Microsoft Sentinel.
What lands in Sentinel
The solution brings your organisation's Deliverd audit log into your Sentinel workspace, in its own DeliverdAudit_CL table:
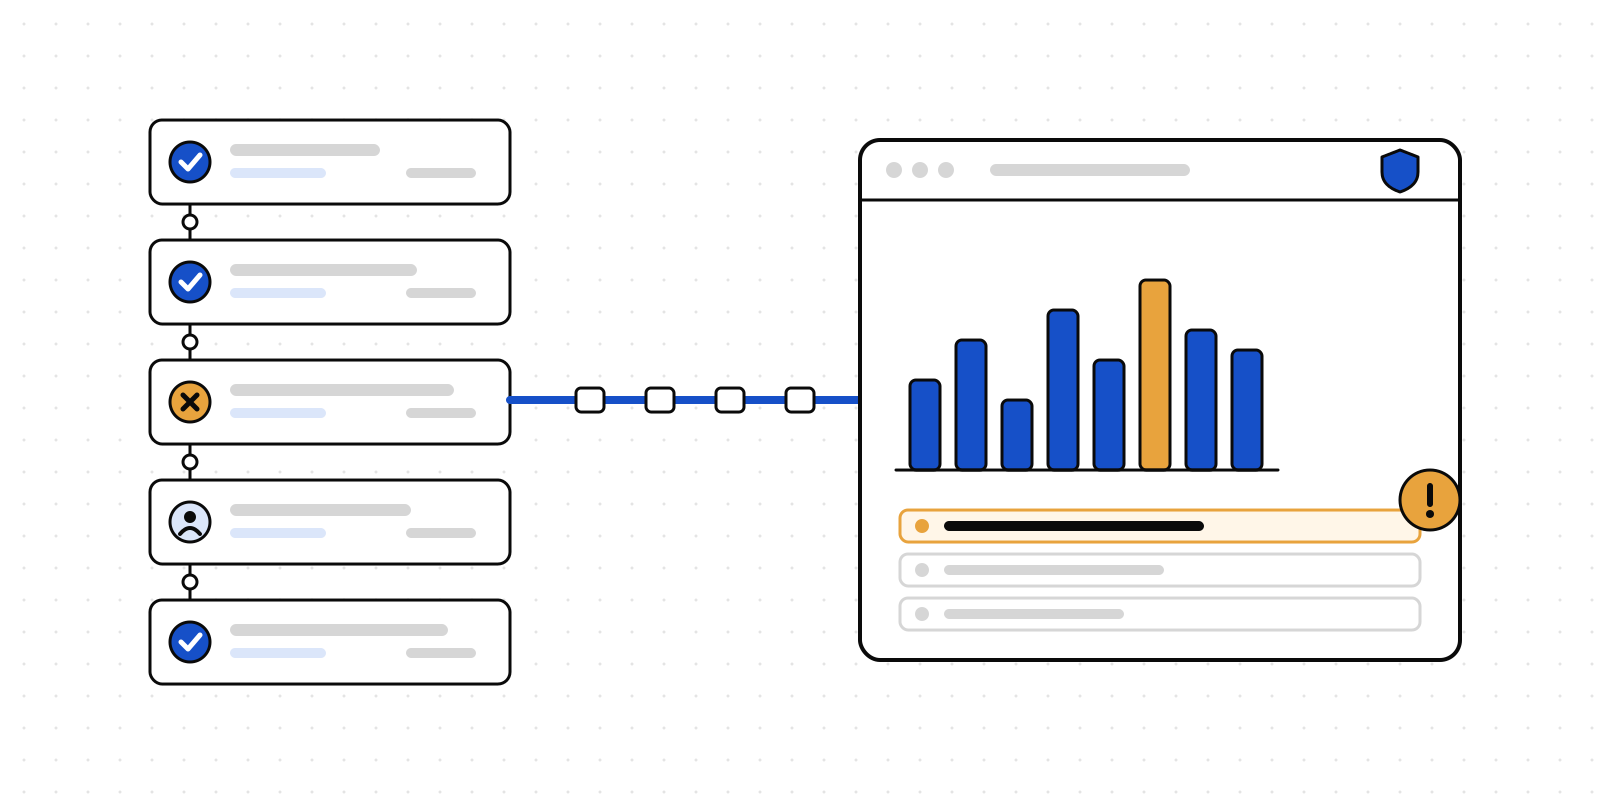
- Every approval, asked for and decided, and who decided it: approved, rejected, changes requested, expired or cancelled.
- Every policy gate, allowed, refused or sent to a person.
- What agents reported doing with a permission, and any report Deliverd refused because the permission didn't cover it.
- Changes that matter to an auditor: policy, tokens, members, evidence exports and legal holds.
Each entry keeps its place in your organisation's hash chain (ChainSeq, PrevHash, RowHash). What Sentinel holds can be checked against Deliverd's own record, so the copy your SOC searches is one your auditors can trust too.
Four rules, ready to go
The solution ships with four analytics rules, switched on by default (or off, if you'd rather review them first):
- An agent reported an act its permission did not cover. High severity, checked every fifteen minutes. This is the one you want to hear about.
- An agent was refused by policy again and again. Medium. An agent that keeps hitting the same wall is either misconfigured or trying its luck, and both deserve a look. The threshold is a single line to tune to your agents' normal rate.
- An API token was used beyond its scopes. Medium. Someone, or something, is probing.
- Policy, evidence or a legal hold changed. Low. The changes an auditor will ask about later, raised now.
There's a workbook too: approvals by outcome, gate decisions over time, the actions refused most often, who does the deciding, and acts refused after the fact.
And because it's all in Log Analytics, your analysts can ask their own questions in KQL. Which actions does policy refuse most?
DeliverdAudit_CL
| where EventType == "gate.denied"
| summarize Refused = count() by Action = tostring(Metadata.action)
| top 10 by Refused
One step to install
No waiting for a marketplace listing and no packaging tools. Deliverd for Microsoft Sentinel installs with a single Deploy to Azure template. You pick the workspace Sentinel runs on, give it your Deliverd address and an API token with audit:read, and one deployment creates the table, the data collection endpoint and rule, the connector with your organisation already connected, the four rules and the workbook. Azure keeps the token as a secure value, so it can't be read back after deployment.
The connector checks Deliverd for new entries every five minutes. The first data can take up to thirty minutes to show up, then it keeps flowing. Running more than one Deliverd organisation? Deploy again with the other organisation's token.
A couple of things we were careful about:
- The audit log is never readable with an agent key. The token has to belong to an owner, administrator or security administrator, and Deliverd checks that role on every call.
- Read-only. Sentinel reads the record. It can't change a decision or a rule in Deliverd.
The same audit log is in the app under Records → Audit log, for the people who'd rather not open Sentinel at all.
Part of our Microsoft launch
Sentinel is one of the integrations arriving in our full Microsoft launch this November, alongside approvals inside Power Automate flows, policy in front of GitHub Copilot, Agent 365 feeding your AI register, and your Purview rules on every AI tool. Microsoft runs your agents. Deliverd decides what they may do, proves who said yes, and now puts that proof where your security team already looks.
Deliverd for Microsoft Sentinel is in preview. We haven't run it in a customer's workspace yet, so if you run Sentinel and want to be among the first, tell us and we'll install it with you.
Deliverd is an independent product. It is not made or endorsed by Microsoft.